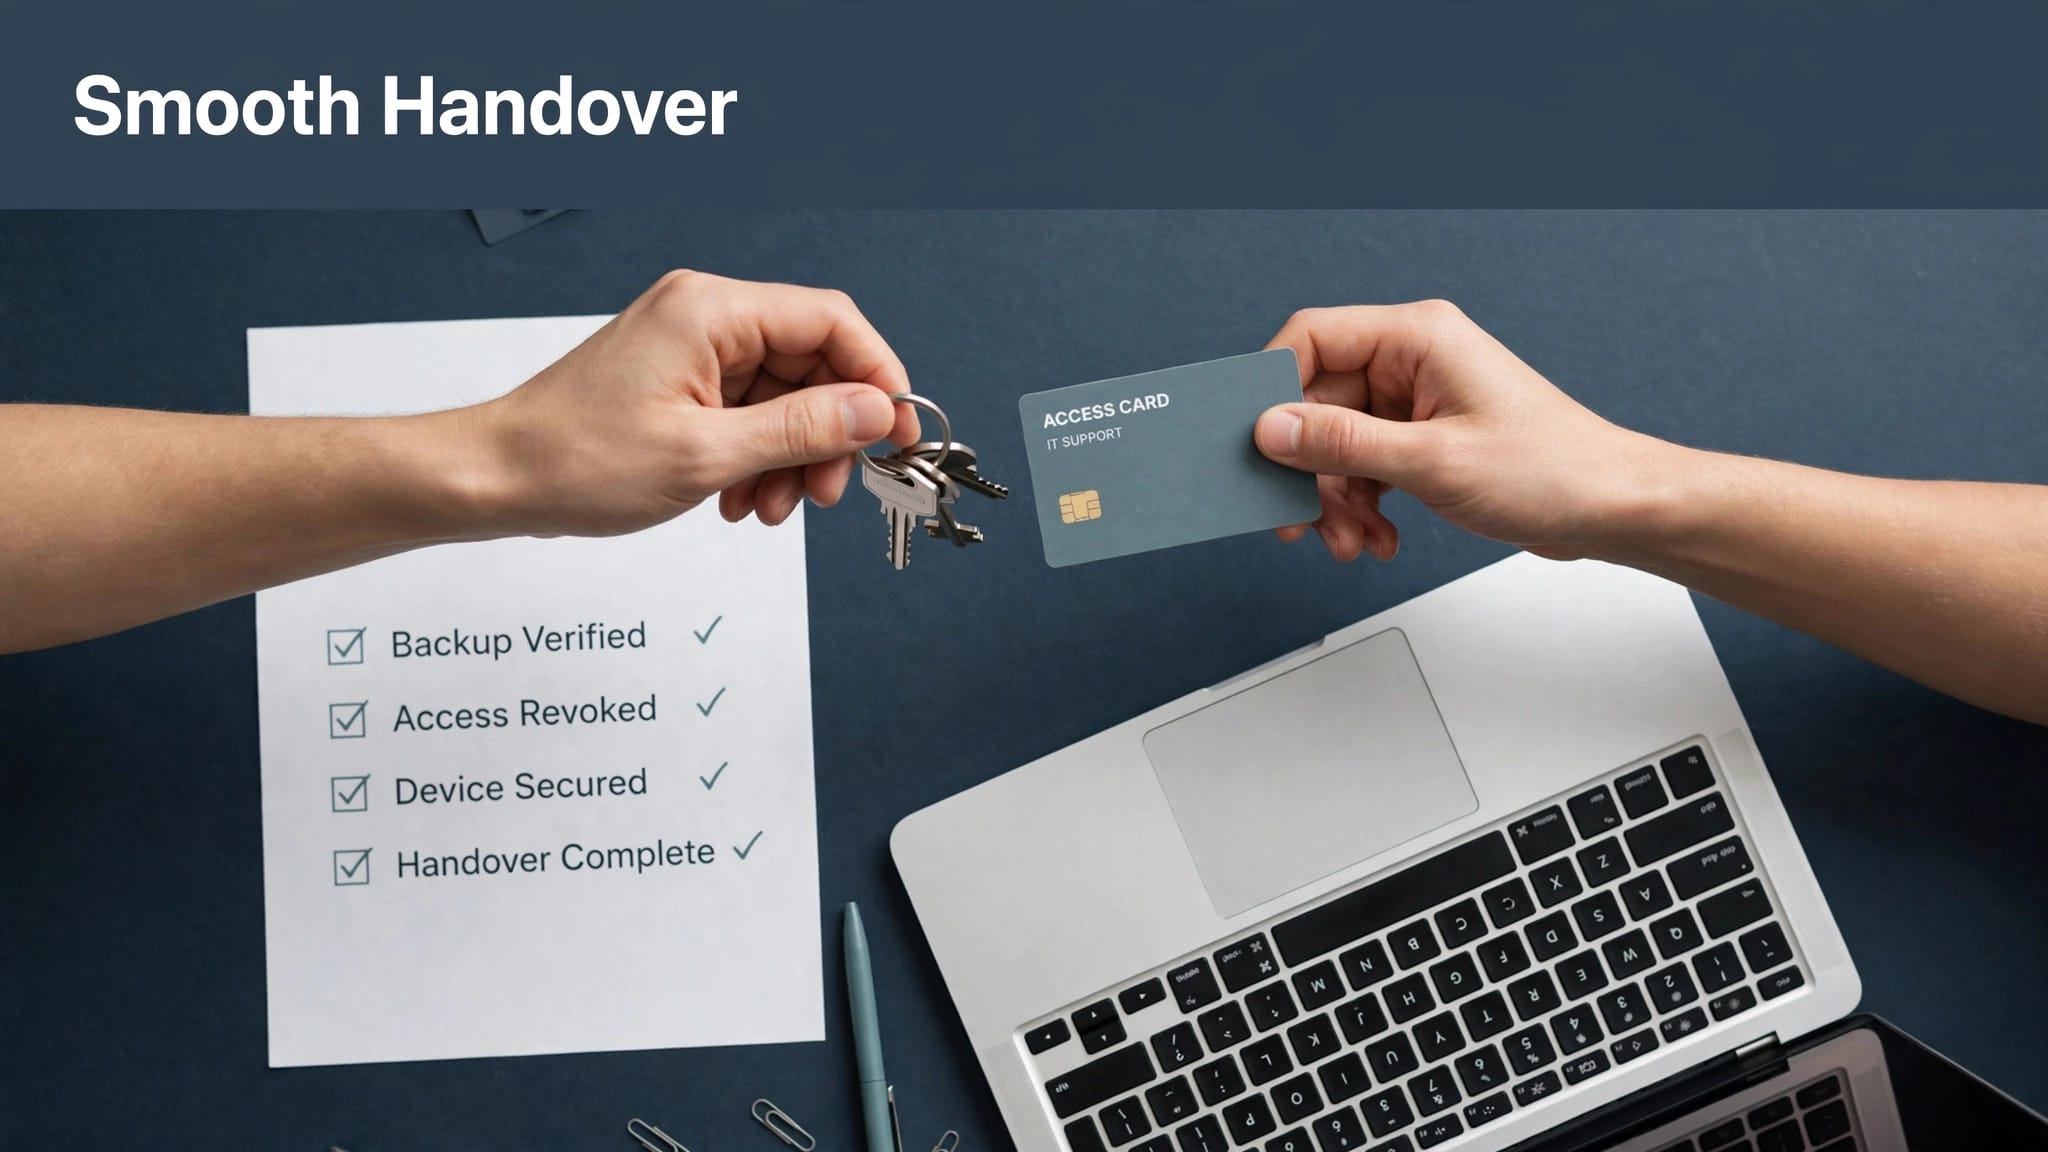

Construction firms can keep site phones, tablets and laptops secure without slowing crews by managing devices centrally and making secure settings the default. In practice, construction site device security should combine encryption, strong sign-in controls, prompt software updates, remote management and consistent device setup. NCSC guidance recommends centralised device management, encryption and enforced updates for organisational devices.
The aim is to make security part of the device rather than another task workers have to remember during a busy day.
What does device security mean on a construction site?
Device security covers the hardware, company data and accounts crews use to read drawings, record progress, take photographs and access business systems. Endpoint security for field teams reduces the chance that a lost handset, stolen laptop or compromised login develops into a wider security incident.
Physical site security still matters, but lost equipment can contain cached project files, customer information and access credentials. Full-disk encryption helps protect data at rest if someone gains physical possession of a device.
Controls that protect without the friction
| Risk on site | Low-friction control |
|---|---|
| Lost or stolen device | Full-disk encryption plus remote or selective wipe where supported |
| Weak or shared logins | MFA and stronger sign-in such as passkeys or biometrics |
| Out-of-date software | Automatic updates with central compliance monitoring |
| Phishing on the move | Filtering plus short guidance to help crews spot a phishing email |
| Inconsistent setup | Standardised device provisioning before equipment reaches site |
The NCSC recommends Mobile Device Management (MDM) as a way to enforce policies, monitor device compliance and remotely manage organisational equipment. It also recommends automatic updating because security patches close known vulnerabilities.
Tools such as Microsoft Intune can bring several controls together. Depending on the platform and configuration, Intune can apply device and application policies, require encryption, restrict movement of company information and remove organisational data remotely. On supported employee-owned devices, app-protection policies can selectively wipe company app data without removing the worker’s personal information.
Remote wipe should complement encryption rather than replace it. NCSC guidance notes that an MDM remote wipe of a lost device generally requires it to be switched on and connected to a data network before the command can be received.
Connectivity also matters on construction sites. Authentication policies need to reflect how teams actually work rather than creating avoidable lockouts when connectivity is limited.
Endpoint hardening provides a secure baseline, while a zero trust approach avoids assuming a device is trustworthy simply because it is connected to a familiar network. Current NCSC guidance emphasises central device management, secure configuration, automatic patching, device identity and visibility of compliance status as foundations for zero-trust access.
Getting the basics owned
A repeatable setup is easier to manage than configuring each device individually. NCSC guidance recommends automated or zero-touch enrolment where possible, helping organisations apply standard configurations as devices are issued.
IT consulting can help define the device policy, standard build and rollout around the way site teams operate. The NCSC’s device security guidance is also a useful independent reference covering configuration, MDM, updates and secure device erasure.
If projects cross borders, European IT support and global IT support for international projects can help maintain consistent device policies across different locations.
Network penetration testing can assess exploitable weaknesses within an agreed scope, but it does not replace device management, patching or access-control reviews.
Construction brings its own challenges, including rugged devices, temporary sites, subcontractors and frequently changing teams. IT support for construction companies should account for those working conditions rather than applying an office-only approach.
Secure the kit, keep the crew moving
Good site device security should be largely unobtrusive. Central management, encryption, automatic updates and appropriate authentication reduce the number of security decisions workers need to make while still protecting company information.
Northern Star supports construction firms with device management, cyber security and managed IT support in London. Call 0800 319 6032 or request a callback to review how your crews’ devices are protected today.