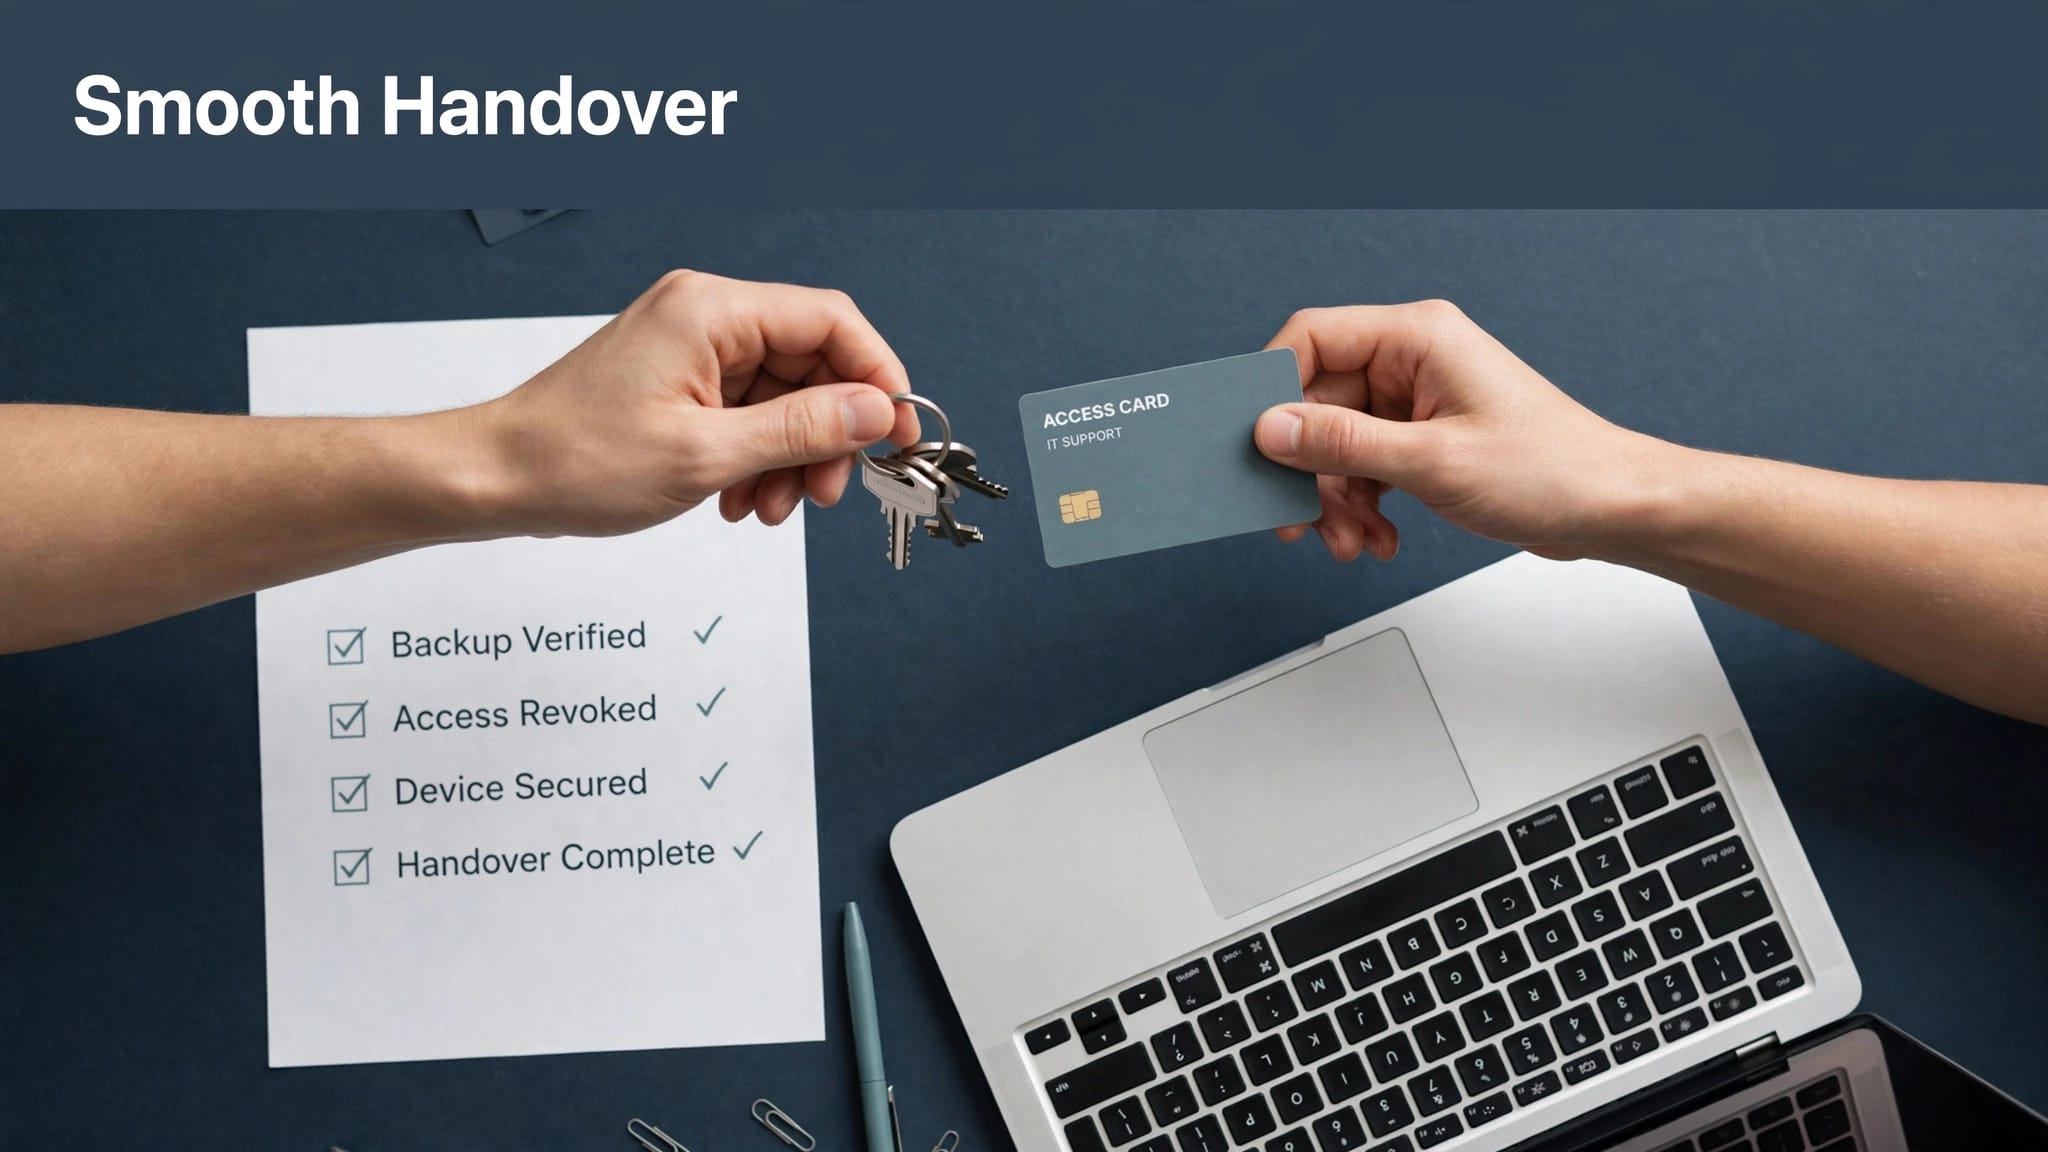

Most Microsoft 365 leaver processes fail because sign-in is blocked but sessions are not revoked, data is removed before ownership is transferred, or access through devices, sharing links and connected apps is overlooked. The sequence matters.
Step one, cut live access properly
Block sign-in, revoke sessions in Microsoft Entra ID and reset the password to a random value. Revoking sessions invalidates refresh tokens, but Microsoft Entra access tokens normally last about one hour. Continuous Access Evaluation can shorten that window for supported Microsoft 365 services, so do not assume blocking sign-in ends every active session instantly.
Then check what a password reset does not necessarily remove: mailbox forwarding and inbox rules, third-party app access, app passwords, and shared or service accounts the person administered. That is where zombie tech can become an offboarding problem.
Step two, deal with data before you delete anything
If colleagues need ongoing email access, convert the user mailbox to a shared mailbox before removing its Exchange licence. An unlicensed shared mailbox is limited to 50GB. Larger mailboxes, archiving and some hold scenarios require appropriate licensing.
For files, identify an owner and transfer what the business needs before deleting the account. Microsoft’s OneDrive retention and deletion guidance confirms the deleted-user cleanup period starts when the user is deleted from Microsoft Entra ID, not when sign-in is blocked or a licence is removed. However, unlicensed OneDrive accounts are now automatically archived on their 93rd unlicensed day. Keep an independent backup; common cloud to cloud backup mistakes explains why.
The checklist
| When | Action | Why it gets missed |
|---|---|---|
| Day 0 | Block sign-in, revoke sessions, reset password | Blocking alone does not immediately invalidate every access token |
| Day 0 | Remove from Teams, SharePoint and security groups | Permissions need separate cleanup |
| Day 0 | Audit mailbox rules, forwarding and connected apps | These can persist after password reset |
| Day 0 | Retire or wipe managed devices as appropriate | Corporate data may remain cached or synced |
| Day 1 | Reassign required OneDrive data | Retained files need a business owner |
| Day 1 | Convert mailbox to shared, then remove licence | Removing the licence first starts Exchange mailbox retention |
| Day 1 | Review external and guest sharing | Links or permissions can remain valid |
| Day 7 | Confirm owners for Teams, Planner and Power Automate flows | Workloads can become orphaned |
| Day 30 | Delete the account once retention is confirmed | Deletion starts OneDrive deleted-user retention |
Sharing links deserve attention. SharePoint content is not automatically removed when its creator leaves, and OneDrive sharing can continue during the deleted-user retention period. Review the changes to SharePoint and OneDrive guest links and revoke access that is no longer required.
The device is half the job
For enrolled devices, Microsoft Intune provides different actions. Retire removes managed company data and settings while preserving personal data. Wipe performs a factory reset and removes personal and organisational data. Choose the action to match device ownership and policy. Getting enrolment and Conditional Access right sits alongside your wider Microsoft Azure and identity services work.
If a device is not managed, you may not have the same remote-removal controls. Personal accounts are another loose end: if corporate credentials have been reused elsewhere, knowing what to do if company credentials appear on the dark web belongs in the same process.
Retention is a legal question, not just a technical one
Do not delete mail or files simply because someone has left. UK organisations may need information for legal claims, regulatory duties or data subject access requests, while data protection law also requires personal data not to be kept longer than necessary. Document retention periods with the appropriate compliance owner. Managing subject access requests becomes harder if relevant data is gone, and Microsoft 365 backup should support retention and recovery independently of Microsoft’s service defaults. This also belongs in business continuity planning.
Managed SOC services can help detect suspicious sign-ins or activity involving accounts that should no longer be active.
Frequently asked questions
Does removing a licence delete the mailbox?
Not immediately. Removing an Exchange Online licence makes the mailbox unavailable and Microsoft retains the associated data for 30 days. Reassigning a licence within that period can restore access. Convert the mailbox to shared before removing the licence if it needs to be retained that way.
How long can you recover a deleted Microsoft 365 user?
A deleted Microsoft Entra user can normally be restored for 30 days. OneDrive has a separate deleted-user retention period, 30 days by default, followed by a further 93 days in a deleted state. Retention policies or holds can alter this lifecycle.
Should you keep paying for a leaver’s licence?
Not automatically. An eligible shared mailbox can operate without its own licence up to 50GB, but larger mailboxes, archiving and hold requirements can require licensing.
Get the process written down once
Most leaver problems are process problems. As a managed service provider in London, Northern Star can document and run your joiner and leaver workflow. If you would rather review your current tenant first, our IT consulting services can audit what access is still open now. Call 0800 319 6032 or book a callback.