Implementing Endpoint Detection and Response (EDR) in your organization involves several key steps. Here’s a general guide to help you get started:
- Assessment and Planning:
- Evaluate your current security posture: Assess existing security tools, policies, and procedures.
- Identify security challenges and risks: Consider common attack vectors, sensitive data assets, and compliance requirements.
- Develop a comprehensive plan: Include goals, timelines, budget considerations, and resource requirements1.
- Choosing the Right EDR Solution:
- Build it yourself: This requires significant effort and a dedicated team to manage and maintain the system.
- Use a Managed Security Services Provider (MSSP): They can handle part or all of the EDR implementation and management.
- Opt for a Managed Endpoint Detection and Response (MDR): This service focuses on improving threat detection and incident response capabilities2.
- Implementation:
- Deploy EDR tools: Install and configure EDR software on all endpoints (desktops, laptops, servers, etc.).
- Integrate with existing systems: Ensure the EDR solution works seamlessly with your current security infrastructure, such as SIEM (Security Information and Event Management) systems.
- Training and Awareness:
- Train your IT and security teams: Ensure they understand how to use the EDR tools effectively.
- Raise awareness among employees: Educate staff about the importance of endpoint security and how they can help protect the organisation.
- Continuous Monitoring and Improvement:
- Regularly update detection rules and algorithms: Keep your EDR solution up to date to detect new threats.
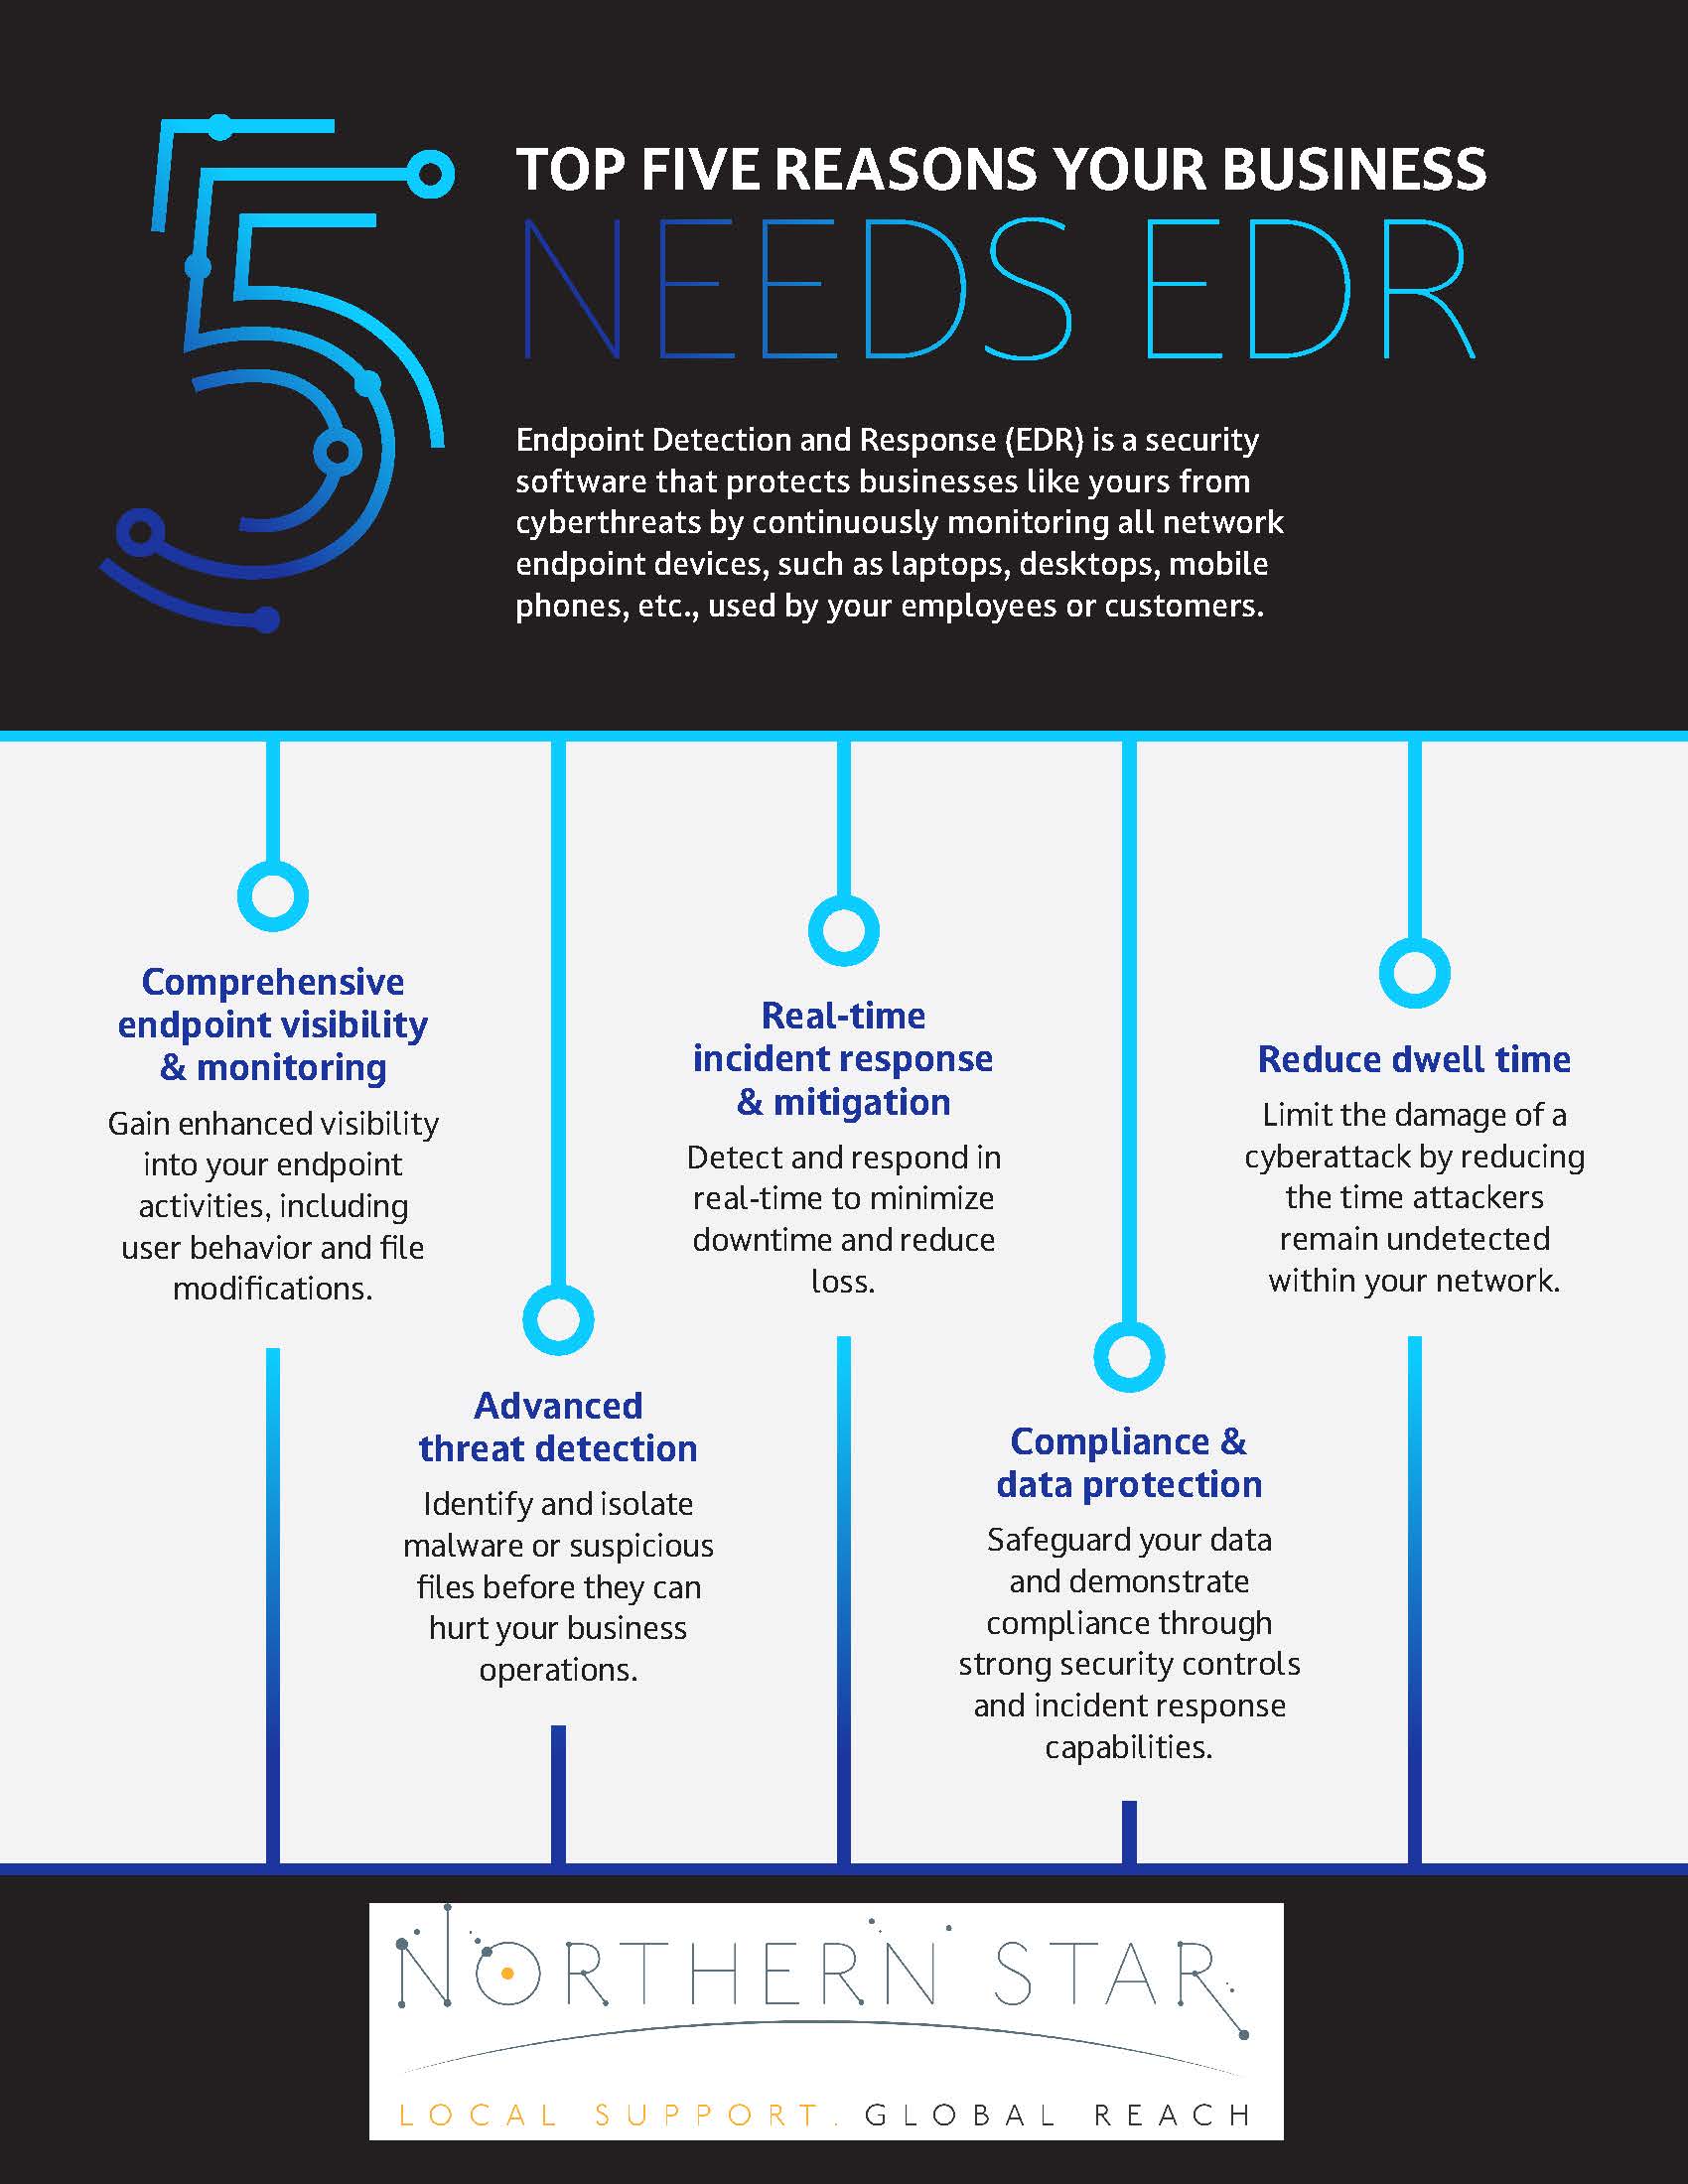
- Monitor and analyse endpoint activities: Use the data collected by the EDR tools to identify and respond to potential threats in real time.
- Incident Response and Mitigation:
- Develop an incident response plan: Outline steps to take when a threat is detected.
- Automate responses where possible: Use the EDR solution to isolate infected endpoints, block malicious processes, and quarantine suspicious files